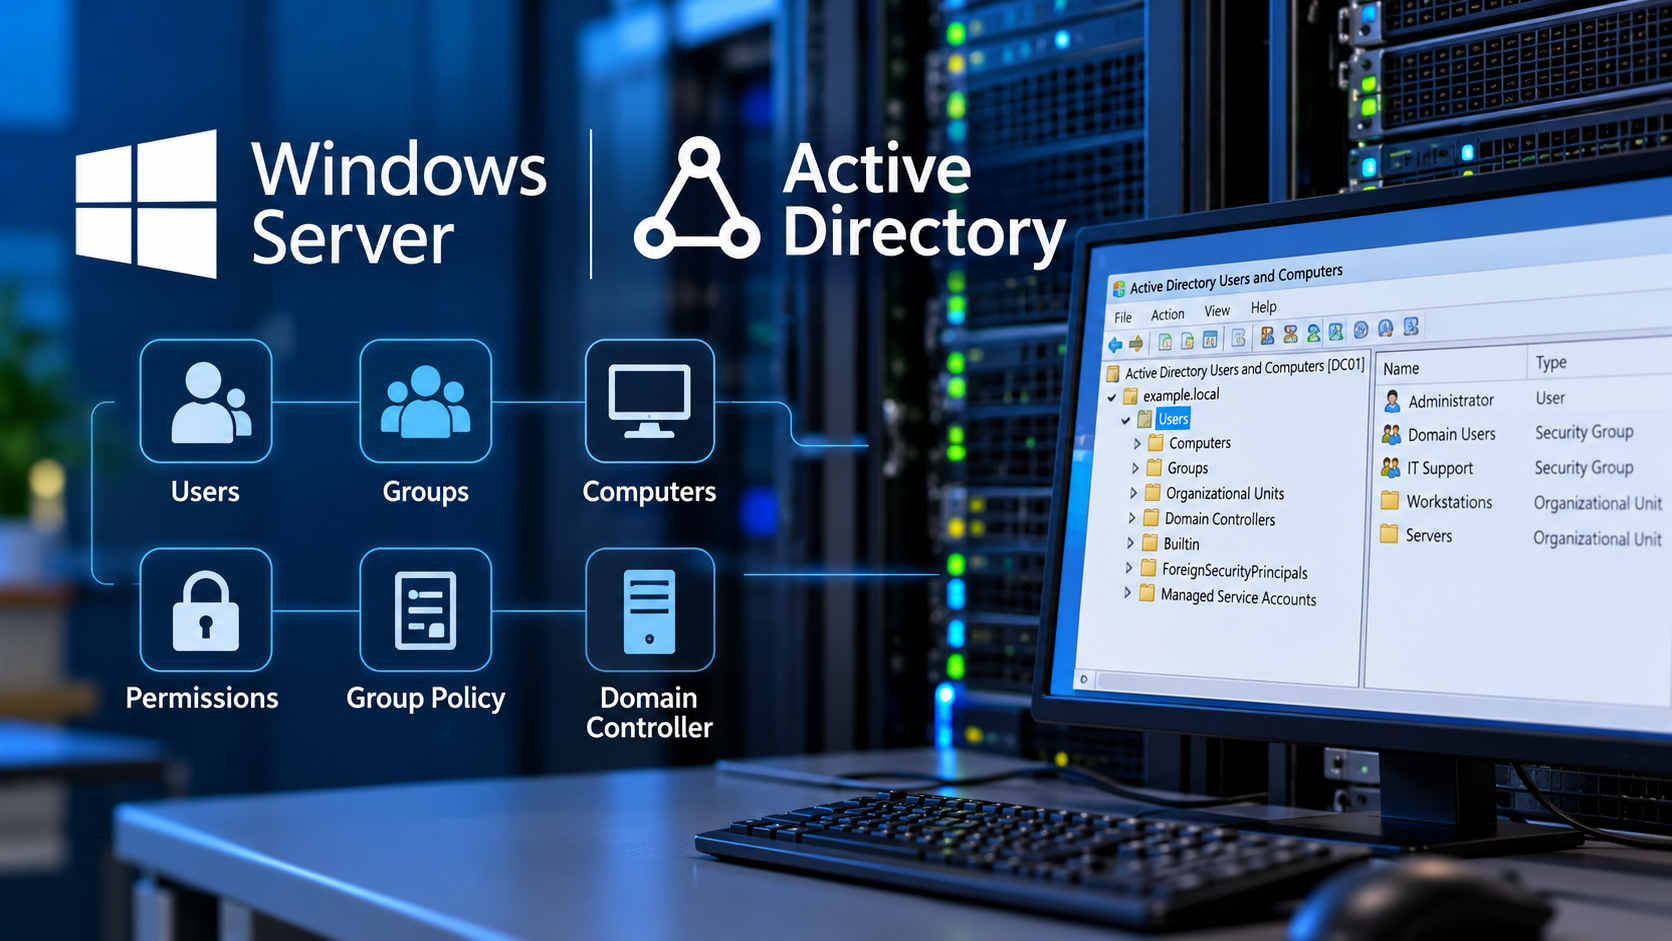
Active Directory is the directory service that underpins identity and access management in most Windows environments. Setting it up correctly from the start saves considerable work later, because the structure chosen early tends to persist. This post covers a standard single-domain setup and the decisions involved.
What Active Directory provides
At its core, AD Domain Services gives you a central place to manage users, computers and permissions. Instead of maintaining separate accounts on every machine, users authenticate once against the domain and receive access according to group membership. Group Policy then enforces configuration consistently across all joined machines.
Before installing
Three things should be settled first, because changing them afterwards is disruptive:
- A static IP address for the server. A domain controller must not change address.
- A domain name. Use a subdomain of a domain you control, such as
corp.example.com. Avoid.local, which causes conflicts with multicast DNS. - DNS planning. AD depends entirely on DNS. The domain controller will normally run the DNS role itself.
Promoting the first domain controller
Install the AD DS role through Server Manager, or via PowerShell:
Install-WindowsFeature -Name AD-Domain-Services -IncludeManagementToolsThen promote the server to a domain controller, which creates the forest:
Install-ADDSForest -DomainName "corp.example.com" -InstallDnsThe server restarts as part of promotion. Afterwards, confirm the DC points at itself for DNS — a surprising number of domain problems trace back to incorrect DNS settings on the controller.
Designing the OU structure
Organisational Units are containers used to organise objects and to target Group Policy. Two approaches are common:
- By function — Users, Computers, Servers, Service Accounts
- By department — Finance, Operations, IT, each with Users and Computers beneath
Keep the hierarchy shallow. Deep nesting makes policy inheritance difficult to reason about, and most of what people reach for OUs to do is better handled by security groups.
Create your own OUs rather than using the default Users and Computers containers — those are containers, not OUs, and Group Policy cannot be linked to them.
Users and groups
Assign permissions to groups, never to individual users. When someone changes role you adjust their group membership rather than auditing every resource they might have been granted directly.
New-ADUser -Name "Example User" `
  -SamAccountName "euser" `
  -UserPrincipalName "euser@corp.example.com" `
  -Path "OU=Users,OU=Finance,DC=corp,DC=example,DC=com" `
  -AccountPassword (Read-Host -AsSecureString "Password") `
  -Enabled $true
Administrators should hold two accounts: a standard account for daily work and a separate privileged account used only for administration. Using a Domain Admin account for routine tasks is one of the most common weaknesses in small environments.
Group Policy
Group Policy applies configuration across the domain. A few principles keep it maintainable:
- Leave the Default Domain Policy for password and account lockout settings only
- Create separate, clearly named GPOs for each distinct purpose
- Link policies at the narrowest scope that achieves the goal
- Document what each GPO is for — the name alone is rarely enough a year later
Use gpresult /h report.html on a client to see which policies actually applied, rather than assuming they did.
DNS checks
Since AD depends on DNS, verify it early:
nslookup corp.example.com
nltest /dsgetdc:corp.example.com
dcdiag /test:dns
Joining a client
Set the client's DNS server to the domain controller's address, then join the domain through System Properties or PowerShell:
Add-Computer -DomainName "corp.example.com" -RestartIf the join fails, DNS is the first thing to check. The client must resolve the domain's SRV records, which it cannot do while pointing at a public DNS server.
Before considering it finished
- Add a second domain controller — a single DC is a single point of failure
- Verify that system state backups complete and can be restored
- Record the Directory Services Restore Mode password somewhere secure
- Confirm time synchronisation; Kerberos fails when clocks drift